Cybersecurity · Open-source product · 2026
OpenLens
See exposure. Preserve evidence. Track change.
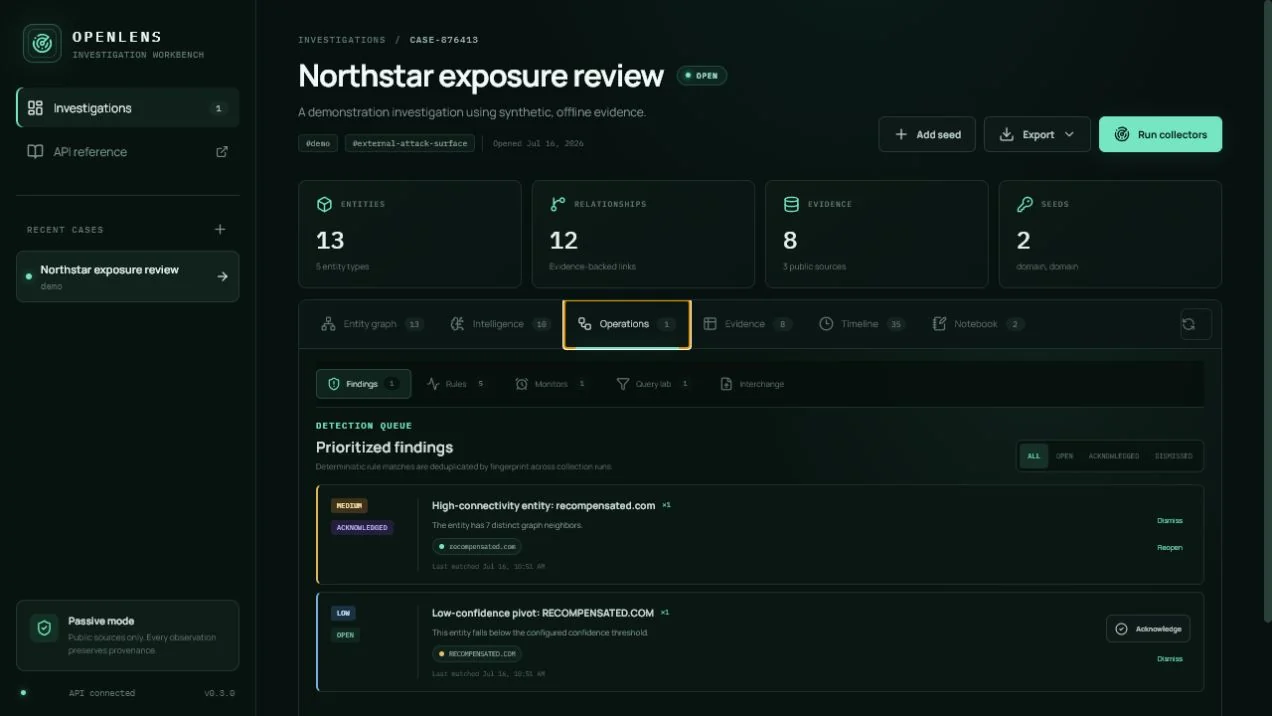
OpenLens consolidates public-source observations into an investigable case without turning passive collection into a promise of certainty.
Deliverables
- Passive collectors
- Case graph
- Evidence trail
- Detection rules
- Change monitoring
- STIX export
01 / Plenty of data, little context.
DNS, RDAP, certificates, and other public sources describe fragments. Without normalization and provenance, the same entity repeats while alerts become detached from evidence.
For defensive public-source research and workflows that require traceability.
02 / A case, not another feed.
Each seed starts a bounded investigation. Entities, relationships, and evidence are normalized, while recurring findings are deduplicated through a stable fingerprint.
Entities, intelligence, operations, evidence, timeline, and notebook remain in the same case, keeping the investigation from fragmenting across tools.
03 / Prioritization that can be explained.
Teams can move from inventory to questions: what changed, which relationship matters, and what evidence supports the observation?
OpenLens is designed for passive observation and defensive analysis. Sources can be incomplete or delayed; findings are signals for review, not verdicts.
01Operations workbench
02Provenance-aware findings
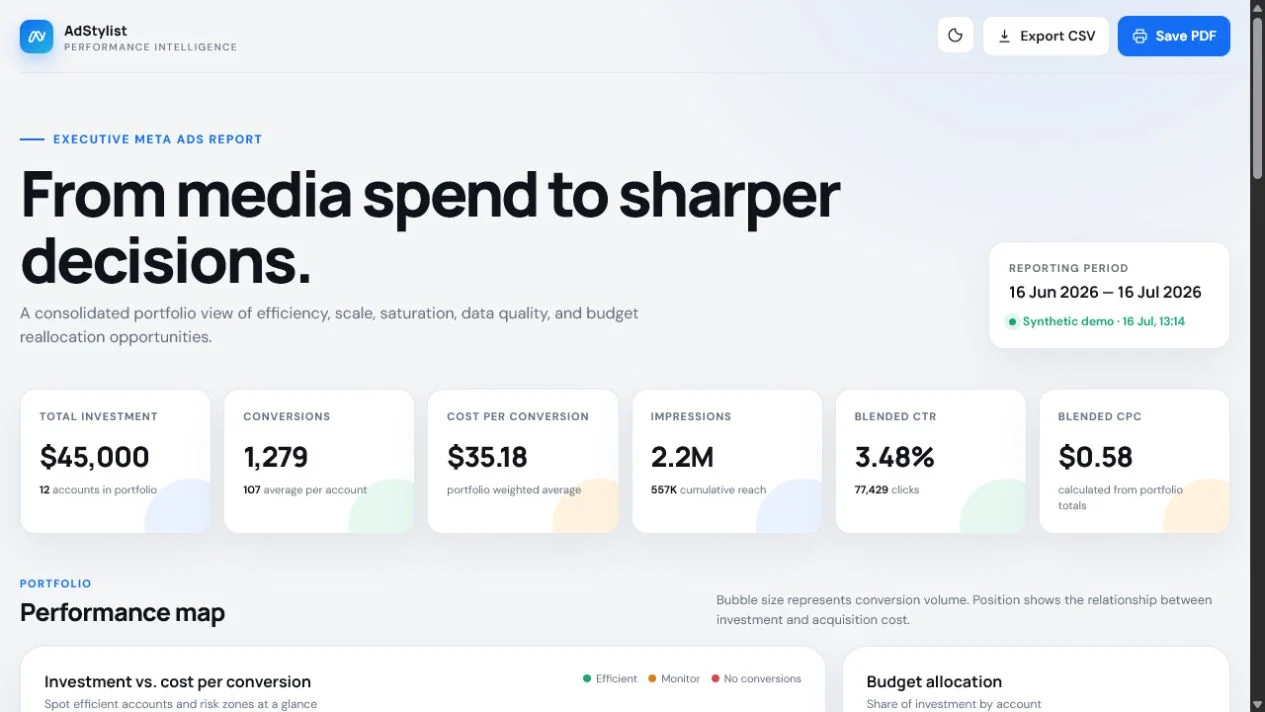
The next signal
Have a project that needs to grow?
Tell us what you are building, what you want to improve, and where you feel stuck.
Start the conversation