AI security · Open-source product · 2026
MCP Sentinel
Control before an AI action becomes an incident.
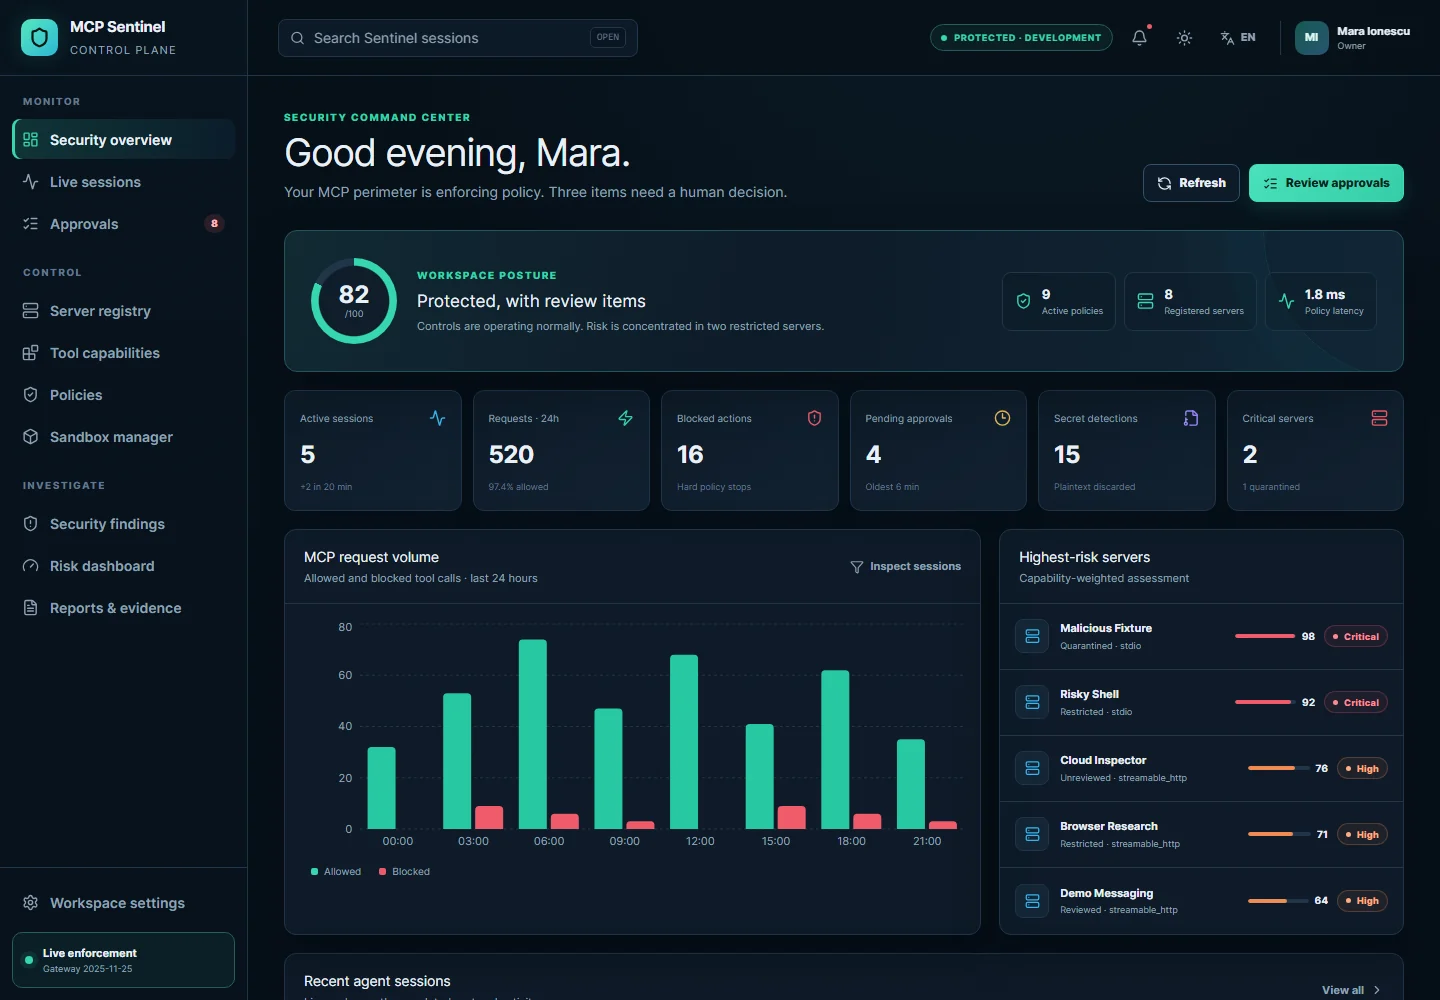
MCP Sentinel turns MCP connections into a governable perimeter: clear policy, explainable risk, human approval, and clean evidence for every action.
Deliverables
- MCP gateway
- Policy engine
- Human approvals
- Secret protection
- Verifiable audit
- Investigation console
01 / Capability is growing faster than control.
Agents can gain access to shells, files, databases, messaging, and deployment. Without one control point, every integration adds risk that is difficult to observe and explain.
For teams that want agent speed but need a clear answer to: who allowed what, why, and with what result?
02 / A gateway that decides, pauses, and documents.
Every request is validated, evaluated through deterministic policy, and inspected for risk. Sensitive actions enter an approval workflow before reaching the server.
Overall posture, waiting approvals, server risk, and session history stay connected. The operator sees context before making a choice.
03 / AI adoption with visible boundaries.
Teams can experiment with agents without turning every connection into a security exception. Control becomes a product capability instead of a scattered collection of rules.
MCP Sentinel reduces risk, but does not guarantee that a client, server, model, or tool is safe. Policy, identity, and isolation depend on correct implementation and operation.
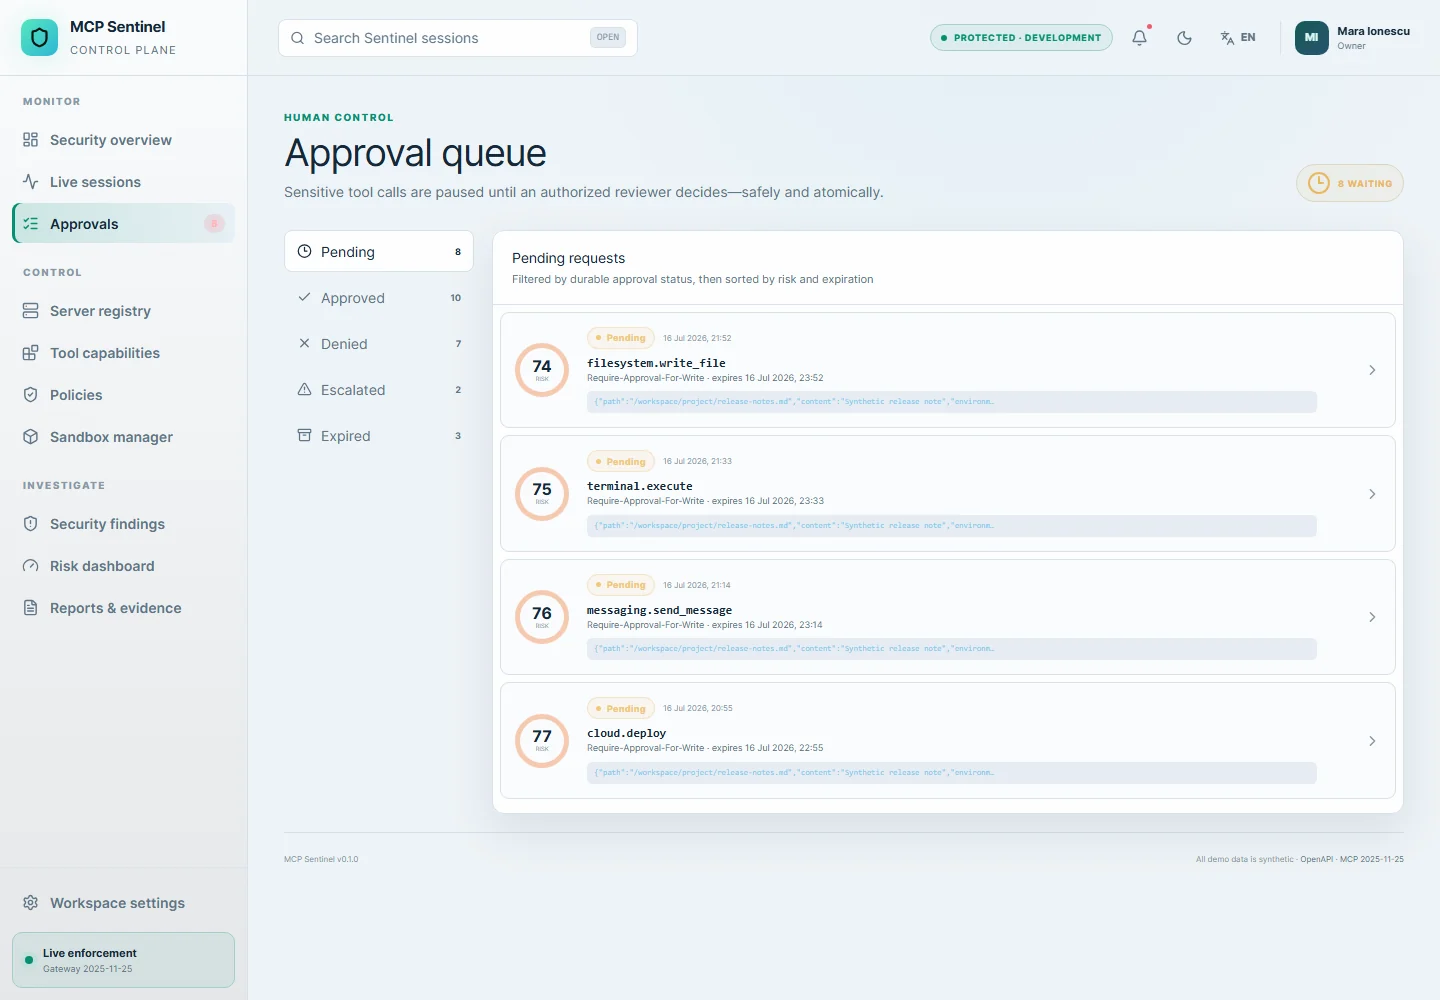
01Approval queue
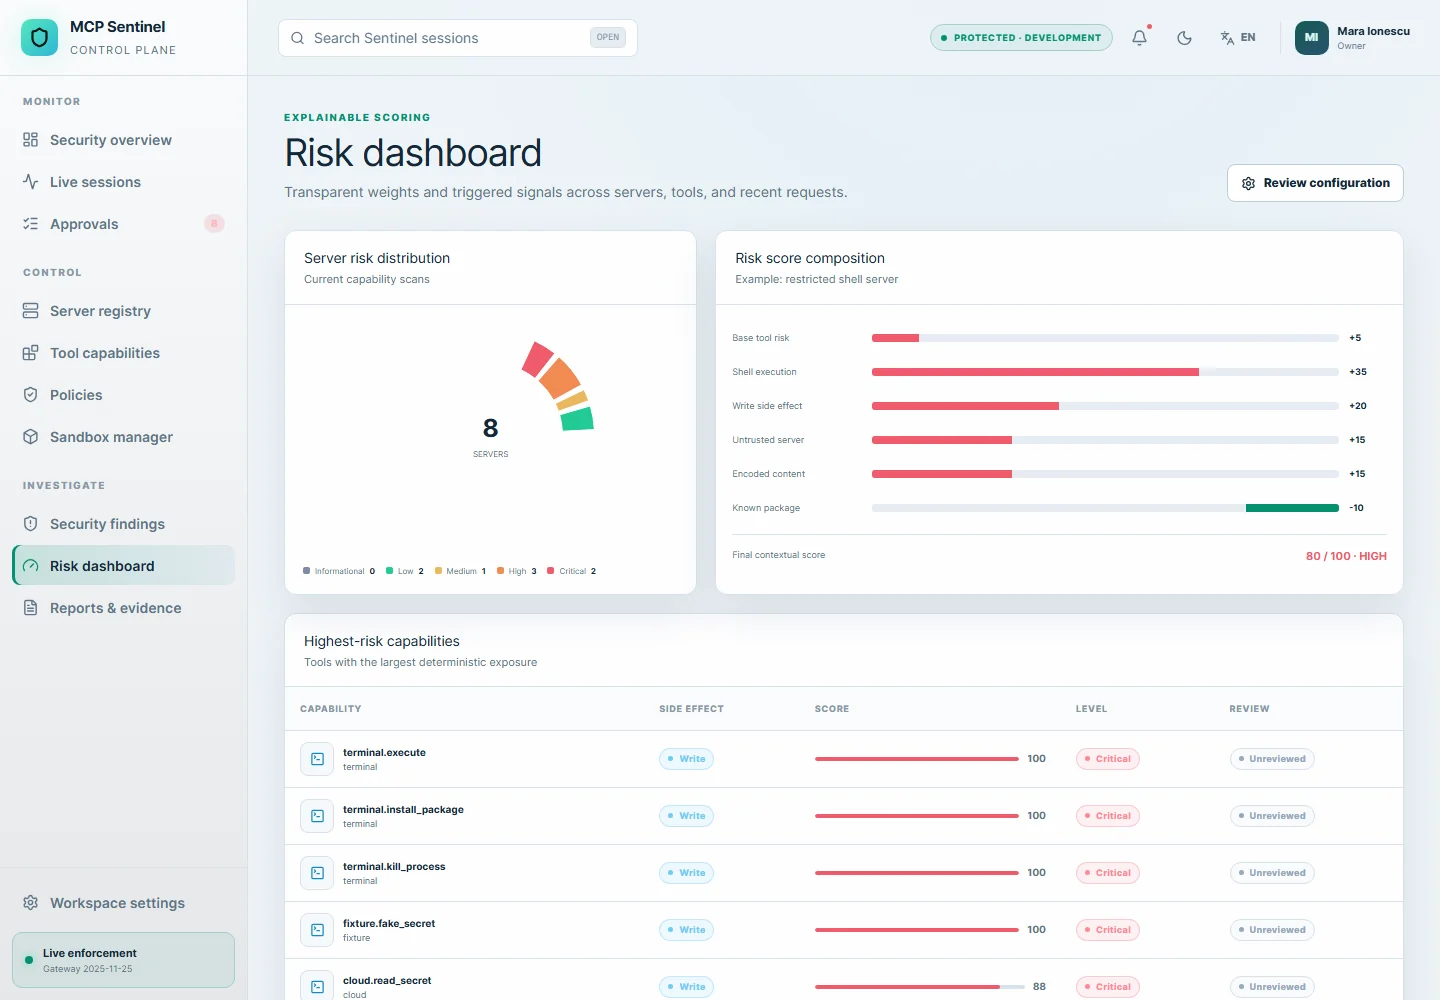
02Explainable risk
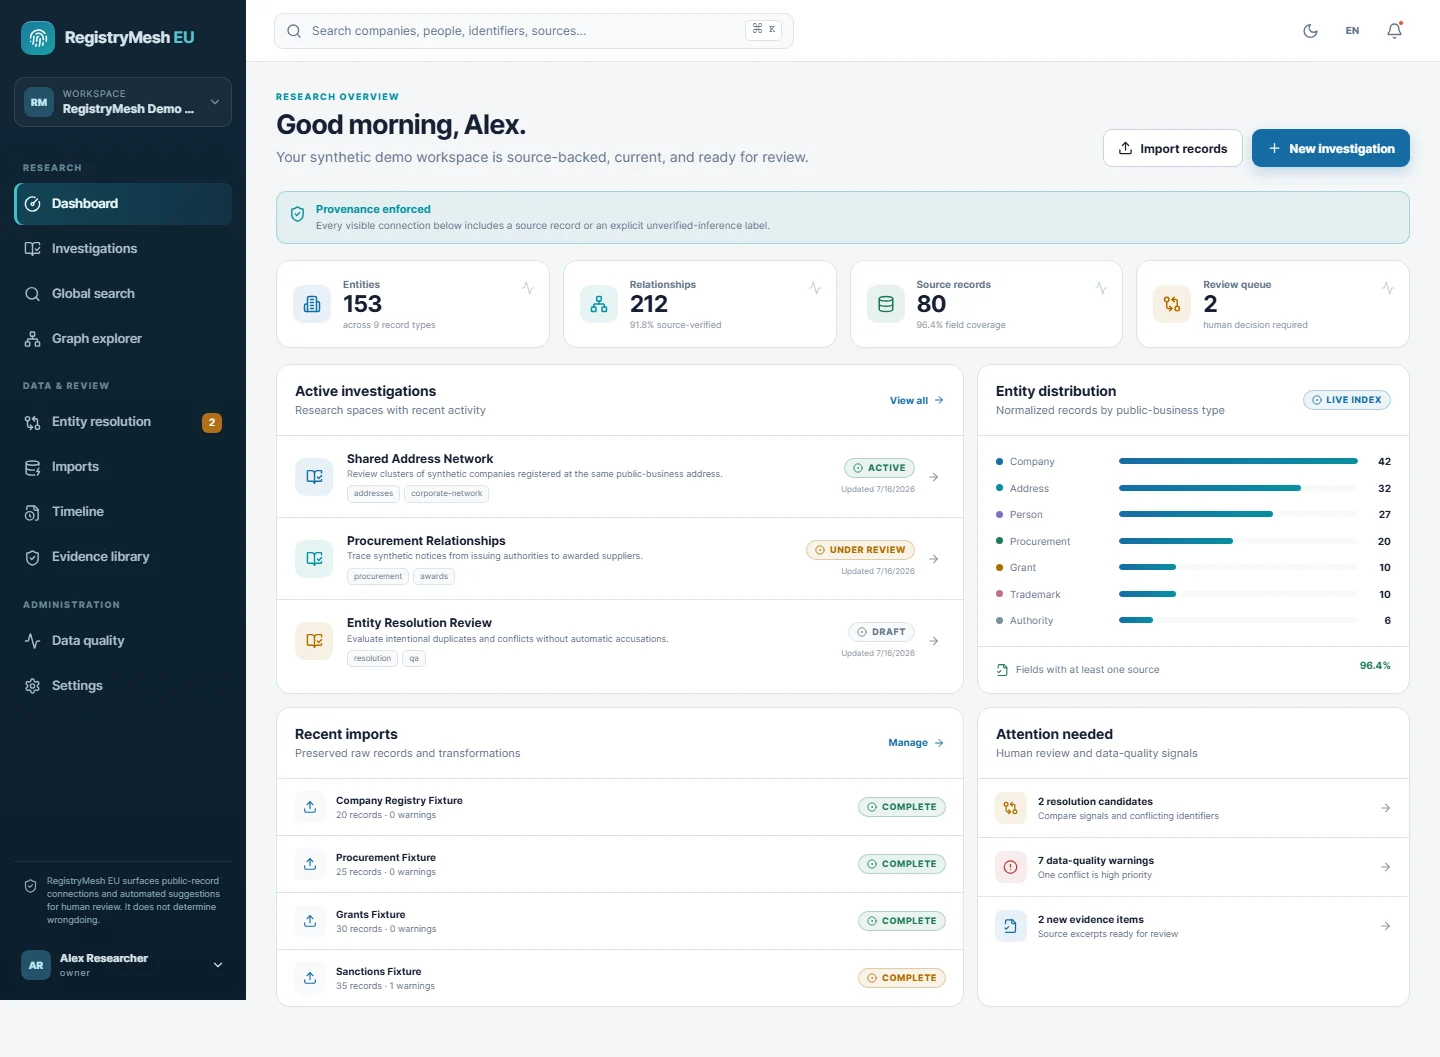
The next signal
Have a project that needs to grow?
Tell us what you are building, what you want to improve, and where you feel stuck.
Start the conversation